
How a helpdesk role could take over the admin: five traps in a web console for Active Directory and OpenLDAP
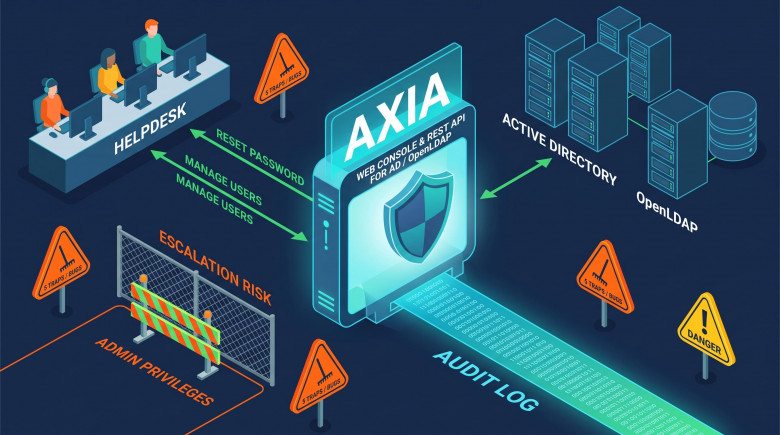
In Axia 0.1.0, a user allowed to edit accounts and move OUs could reset an administrator’s password in four requests. None of the four broke the rule written to prevent exactly that.
Axia is an open-source web console and REST API for Active Directory and OpenLDAP (.NET 10, React). It exists for a routine every company with a directory knows: create an account, reset a password, add someone to a group, disable a leaver. That work belongs with helpdesk, but helpdesk must not be able to promote itself, and every action must leave a trace.
This is not a feature tour. It is five places where the obvious implementation turned out to be a hole or a bug, and what fixed each one. Most of them have nothing to do with Axia: anyone who builds access control on top of LDAP will run into them.


